Settings
The appliance’s Settings page holds appliance-wide preferences and administrative actions, distinct from per-surface configuration. Tab visibility is gated by three separate permissions, not a single role check: System, Admin, Networking, and Security require the settings-management permission; Users requires the separate user-management permission; T&C Manager requires the terms viewing permission; User and Limits are visible to every signed-in user. All three permissions belong to the Administrator role, so these gates show the same tabs to the same people.
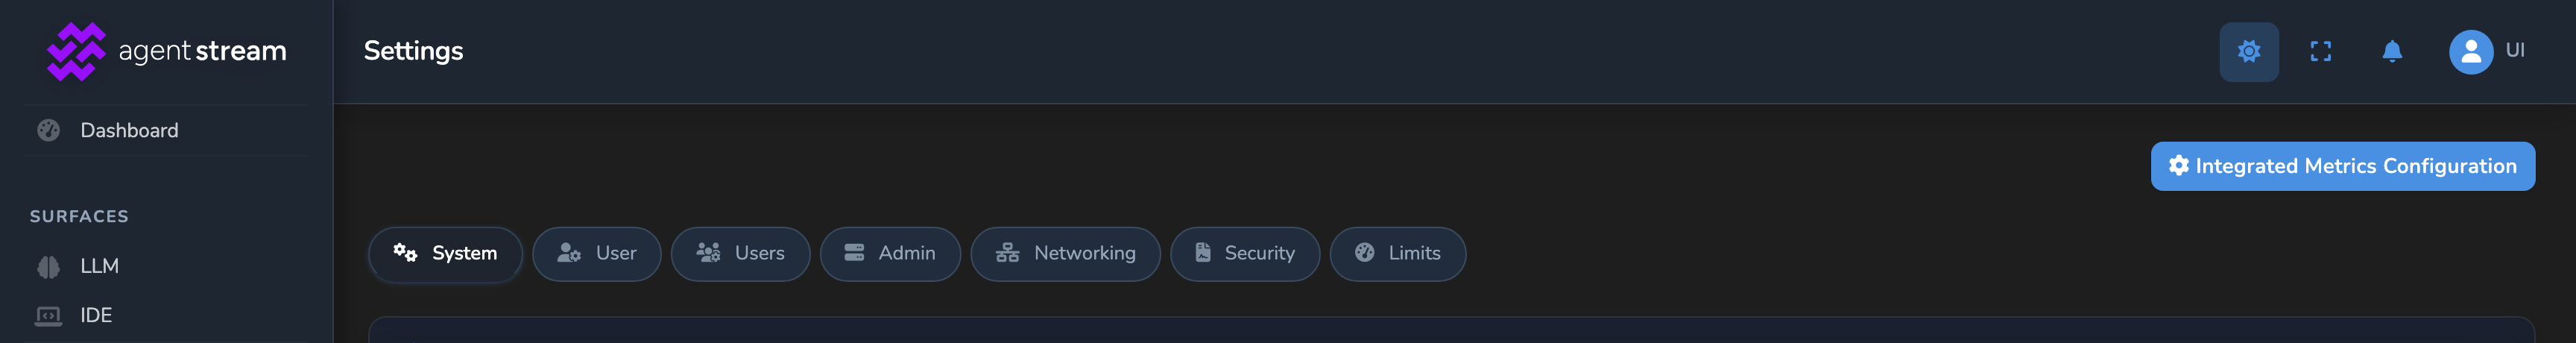
System tab (Administrator)
This tab holds appliance-wide windows and retention periods behind the dashboard’s own live metrics (connection counts, latency, throughput), trading off how far back the dashboard can look against how much memory it spends holding that history. The defaults suit most appliances; adjust once you know your own traffic pattern.
- Shorten Metrics Retention Period, Total Connections Window, or Average Latency Window on a busier appliance to bound memory use and keep figures current. Shortening Average Latency Window specifically right after a change you’re watching closely keeps it reflecting only recent behaviour.
- Raise Temporary Channel Timeout only if your onboarding flow routinely needs longer than 30 seconds to complete.
| Field | Default | Description |
|---|---|---|
| Metrics Retention Period (minutes) | 6 hours | How long to keep connection and rule-validation metrics. Range: 1 minute–7 days. |
| Task Activity Scope (seconds) | 60 seconds | Time window for calculating task throughput; recent activity resets the window. Range: 10–600 seconds. |
| Temporary Channel Timeout (seconds) | 30 seconds | How long a temporary onboarding channel stays active before automatic deletion. Range: 10–300 seconds. |
| Total Connections Window (minutes) | 60 minutes | Sliding window for the total-connections count. Range: 1 minute–24 hours. |
| Average Latency Window (minutes) | 60 minutes | Sliding window for average-latency calculations. Range: 1 minute–24 hours. |
User tab
Personal preferences. These override the system defaults for your own dashboard session only.
| Field | Default | Description |
|---|---|---|
| Badge Time Threshold (minutes) | 5 minutes | Identities created or used within this time show a “new” or “active” badge. Range: 1 minute–24 hours. |
| Auto-Refresh Interval (seconds) | 5 seconds | Minimum time between dashboard data refreshes. Range: 1–300 seconds. |
| Log Timestamp Format | Local Time | Dropdown for log entry timestamps on the Logs page: Local Time, UTC (ISO 8601), Relative, or Compact. |
| Time Series Bucket Interval | 30 seconds | Default bucket interval (choose from 30 seconds up to 6 hours) for the aggregated connections time-series graph; can be overridden on the graph itself. |
| Minimum Payment Items to Display | 10 | Minimum number of payment items shown on the Payments page. |
Users tab (Administrator)
Dashboard account management for every user’s account, distinct from the singular User tab above, which holds only your own personal preferences. Administrator-only.
| Action | Description |
|---|---|
| Filter by role | Show only Administrator, Power User, or User accounts, or all of them. |
| Filter by status | Show only New, Approved, or Disabled accounts, or all of them. |
| Quick-approve | Approves a pending (New) account in place, without opening it for edit. |
| Edit | Opens an account for editing. |
| Delete | Removes an account. Not available for Administrator accounts. |
Admin tab (Administrator)
Metrics/log housekeeping, plus the appliance’s Backup and Restore actions, covered in full in Backup and encryption →.
- Backup (under “Full Storage Backup”) gives you a restorable copy of the appliance’s configuration and data: run it before a risky change, or on a schedule as a disaster-recovery snapshot. It excludes
logsandsystem_metrics, since those are ephemeral and regenerate at runtime. - Restore (under “Restore from Backup”) rolls an appliance back to a previous backup, onto the same appliance it came from. Validation runs synchronously on upload, before anything is touched; a cross-domain, malformed, or otherwise invalid backup is rejected immediately with no storage mutation and no restart.
| Action | Description |
|---|---|
| Truncate Old Metrics Now | Removes metrics older than the retention period immediately. |
| Truncate Old Logs | Removes old and rotated log files. The current active log file is always kept. |
| Backup | Downloads an encrypted backup of the appliance’s storage as a single file, excluding logs and system_metrics. |
| Restore | Uploads a backup file to restore. The upload is validated immediately (domain, integrity, format); once accepted, the appliance restarts and replaces its current storage with the backup. A backup doesn’t include the appliance’s logs or system metrics, so restoring one clears the current logs and system metrics. |
Networking tab (Administrator, read-only)
Shows the appliance’s inbound mTLS / client-certificate settings. These values are fixed for your appliance and shown read-only.
| Field | Description |
|---|---|
| Direct TLS client-cert request | Whether the appliance’s own TLS handshake asks for a client certificate: Disabled, Optional, or Required. |
| Trusted proxy CIDRs | Peer IPs allowed to present a forwarded client certificate header. Empty means the forwarded-cert path is disabled. |
| Forwarded client-cert header | The header name and wire format read when the peer matches a trusted proxy CIDR. The row is always shown; when no trusted proxy is configured, it displays an explanatory message instead of a header name. |
Security tab (Administrator)
Turn this on when you need a durable, queryable record of every allow/deny policy decision, whether for a compliance review or to investigate a specific denial after the fact. Structured logs and metrics are always emitted regardless of this switch, so leaving it off costs you only the durable audit-log entry, not observability itself.
| Field | Default | Description |
|---|---|---|
| Record policy decisions to the audit log | Off | Toggle. Records a durable, redacted entry for every allow/deny policy decision (pipe, IDE, gateway, and surface), viewable on the Audit page. |
Limits tab
Read-only. Lists every configured appliance resource limit alongside its current usage. Reaching a limit prevents creating more of that entity until you upgrade your appliance tier.
T&C Manager tab (Administrator)
Shows the Affinidi Terms that apply to the appliance, and lets you publish your own organisation’s terms and conditions for users to accept at sign-in.
- Affinidi Terms shows the title and version of the Affinidi Terms. It is read-only.
- Customer T&C publishes your own terms. Publishing a new version replaces the current one, and Deactivate stops requiring them. Published versions and acceptance records are kept.
- Published history lists every published version with its Title, Version, whether Re-consent was required, and a link to the Document.
Deactivate asks for confirmation with Confirm deactivation, then stops requiring your terms. The tab shows “Customer T&C deactivated.”, and the Customer T&C card shows no current version until you publish a new one.
| Field | Default | Description |
|---|---|---|
| Title | Not set | The name of your terms, shown to users. |
| Version | Not set | A version you haven’t published before. Enter a new version when the content or URL changes. |
| HTTPS document URL | Not set | Where your terms document is published. |
| Require existing users to accept this version at their next login | On | When on, users who accepted an earlier version must accept this one at their next sign-in. |
Related
- Backup and encryption: The backup and restore file format behind the Admin tab’s actions.
- RBAC: Which role can see the administrator-only tabs.
- Limit dashboard actions with RBAC roles: Assign the role that decides which accounts appear, and what they can do, on the Users tab.
- Cost and usage governance: How appliance tier limits fit alongside spend-based budgets.
- Require terms acceptance before dashboard access: Publish your own terms on the T&C Manager tab and ask users to accept them at sign-in.
Glad to hear it. Thanks for letting us know.
Sorry to hear that. Thanks for letting us know.