Managed Agent
The Managed Agent node defines the single upstream destination the gateway forwards traffic to. Every surface has exactly one Managed Agent. The properties panel covers endpoint routing and authentication. Policy enforcement, networking resilience, MCP tool access policies, Trust Check queries, and identity extraction each require a separate canvas element added to the surface. Reference pages for each element are linked from the canvas table below.
Managed Agent node fields
These fields appear directly in the Managed Agent properties panel when you select the node on the canvas.
| Field | Type | Required | Default | Description |
|---|---|---|---|---|
| Endpoint Type | select | Yes | Direct URL | How the upstream destination is addressed. Options: Direct URL, via Gateway Connection, via MCP Proxy (MCP surfaces only), via A2A Proxy (A2A or AP2 surfaces only). |
| Target Endpoint URL | string | Yes (Direct URL) | — | Full upstream URL. See Endpoint schemes. |
| Gateway / Agent Surface on Gateway | select | Yes (via Gateway Connection) | — | Remote gateway and the agent surface on it to route to. Builds a fabric:// endpoint automatically. |
| MCP Proxy | select | Yes (via MCP Proxy) | — | MCP proxy to front this agent’s tools. Builds a proxy:// endpoint automatically. |
| A2A Proxy | select | Yes (via A2A Proxy) | — | Managed A2A proxy that adapts this surface to a non-A2A backend. Builds an a2a-proxy:// endpoint automatically. The surface’s A2A versions show on its Access Point, and the proxy’s Agent Card tab explains them. See A2A proxy Targets. |
| Display name | string | No | — | Cached name shown in the dashboard for fabric:// endpoints when the remote gateway is offline. |
| Target Authentication | select | No | None | Service-level credentials the gateway injects into requests forwarded to the target. On a Direct URL endpoint, they also go with the agent card fetch. On via Gateway Connection, the request reaches the agent through the remote gateway, and the Agent Cards view shows “The remote gateway signs in” for the card fetch. The Authentication Type options are None, Bearer Token, Basic Auth, API Key, and Custom. Any option except None shows Configure…, which opens the fields in the Target Authentication table. Not available on MCP Proxy or A2A Proxy endpoint types. |
| Send signed identity VP to target | bool | No | true | When enabled, the gateway signs and injects a Verifiable Presentation into each outbound request carrying the resolved agent identity and caller context. See Identity element reference. |
Target Authentication
Configure… opens the Target Authentication editor. Credential Source decides where the credential comes from: a fixed value in a secret, or a token that the gateway obtains from a credential provider and renews before it expires. Use a provider when the target accepts only short-lived OAuth tokens, such as a Google service account token or an Entra token. See Call an agent protected by Entra or Google OAuth tokens.
| Field | Required | Default | Description |
|---|---|---|---|
| Credential Source | Yes | Static secret | Static secret or Credential provider. |
| Secret | Yes (Static secret) | — | The secret that holds the credential. |
| Credential Provider | Yes (Credential provider) | — | The provider that issues the token. The list offers Client Credentials, JWT Bearer, Client Credentials JWT, and API Key providers, the types that need no user. |
| Authentication Type | Yes | Bearer Token | How the credential is formatted in the header: Bearer Token, Basic Auth, API Key, or Custom. |
| Header Name | No | Authorization, or X-API-Key for API Key | The HTTP header the credential goes in. |
| Header Format | No | — | Shown for Custom. The header value, with {value} in place of the credential. |
| Fallback Behavior | No | Reject request (502 Bad Gateway) | What happens when the secret or provider token can’t be resolved: Reject request (502 Bad Gateway) or Pass through without credentials. |
Delegated Credentials
A Delegated Credentials section appears in this panel when the endpoint uses the fabric:// scheme (via Gateway Connection) and the surface has a Credential Delegation element with at least one credential binding. It controls whether the caller’s delegated access token travels to the remote gateway on this route.
| Field | Type | Required | Default | Description |
|---|---|---|---|---|
| Send delegated credentials over Fabric | switch | No | Off | When on, the caller’s delegated access token from the surface’s Credential Delegation bindings is sent to the remote gateway with each request on this route, and the panel warns that the token is sent to the named receiving gateway. When off, the remote gateway receives no delegated credential. The caller’s own token is always removed before the request crosses Fabric, and the refresh token stays on this gateway. On this route, only MCP requests using protocol revision 2026-07-28 carry the token. |
Each surface variant keeps its own setting, so turn the switch on in every variant whose remote gateway needs the token.
Send delegated credentials over Fabric is off unless it is turned on for a route, including on existing fabric:// routes. If the remote gateway relies on receiving the caller’s delegated token, turn the switch on for that route and save the surface.
MPP Auto-Pay
An MPP Auto-Pay section appears in this panel when the Target Endpoint URL uses the fabric:// scheme, on a gateway build with the MPP payment feature enabled. It is not present on the standard managed-hosting dashboard; a self-hosted deployment enables it by building the dashboard with REACT_APP_ENABLE_MPP_PAYWALL=true.
| Field | Type | Required | Default | Description |
|---|---|---|---|---|
| Automatically pay MPP challenges | bool | No | Off | Automatically pays an MPP payment challenge from a fabric:// target without requiring the original caller’s involvement. |
| Max amount per request | string | No | — | Shown when auto-pay is on. Safety cap on the amount auto-paid per request, for example 0.01. |
Agent Cards view
On a saved A2A or AP2 surface, the Managed Agent panel shows a card fetch line, such as Card fetch: OK or Card fetch: failing, with the cause in brackets, and a View agent cards link. The link opens the Agent Cards view, which is also in the surface editor’s sidebar. Use it to check that the gateway can fetch your agent’s card and to see how the gateway rewrites that card before serving it to callers.
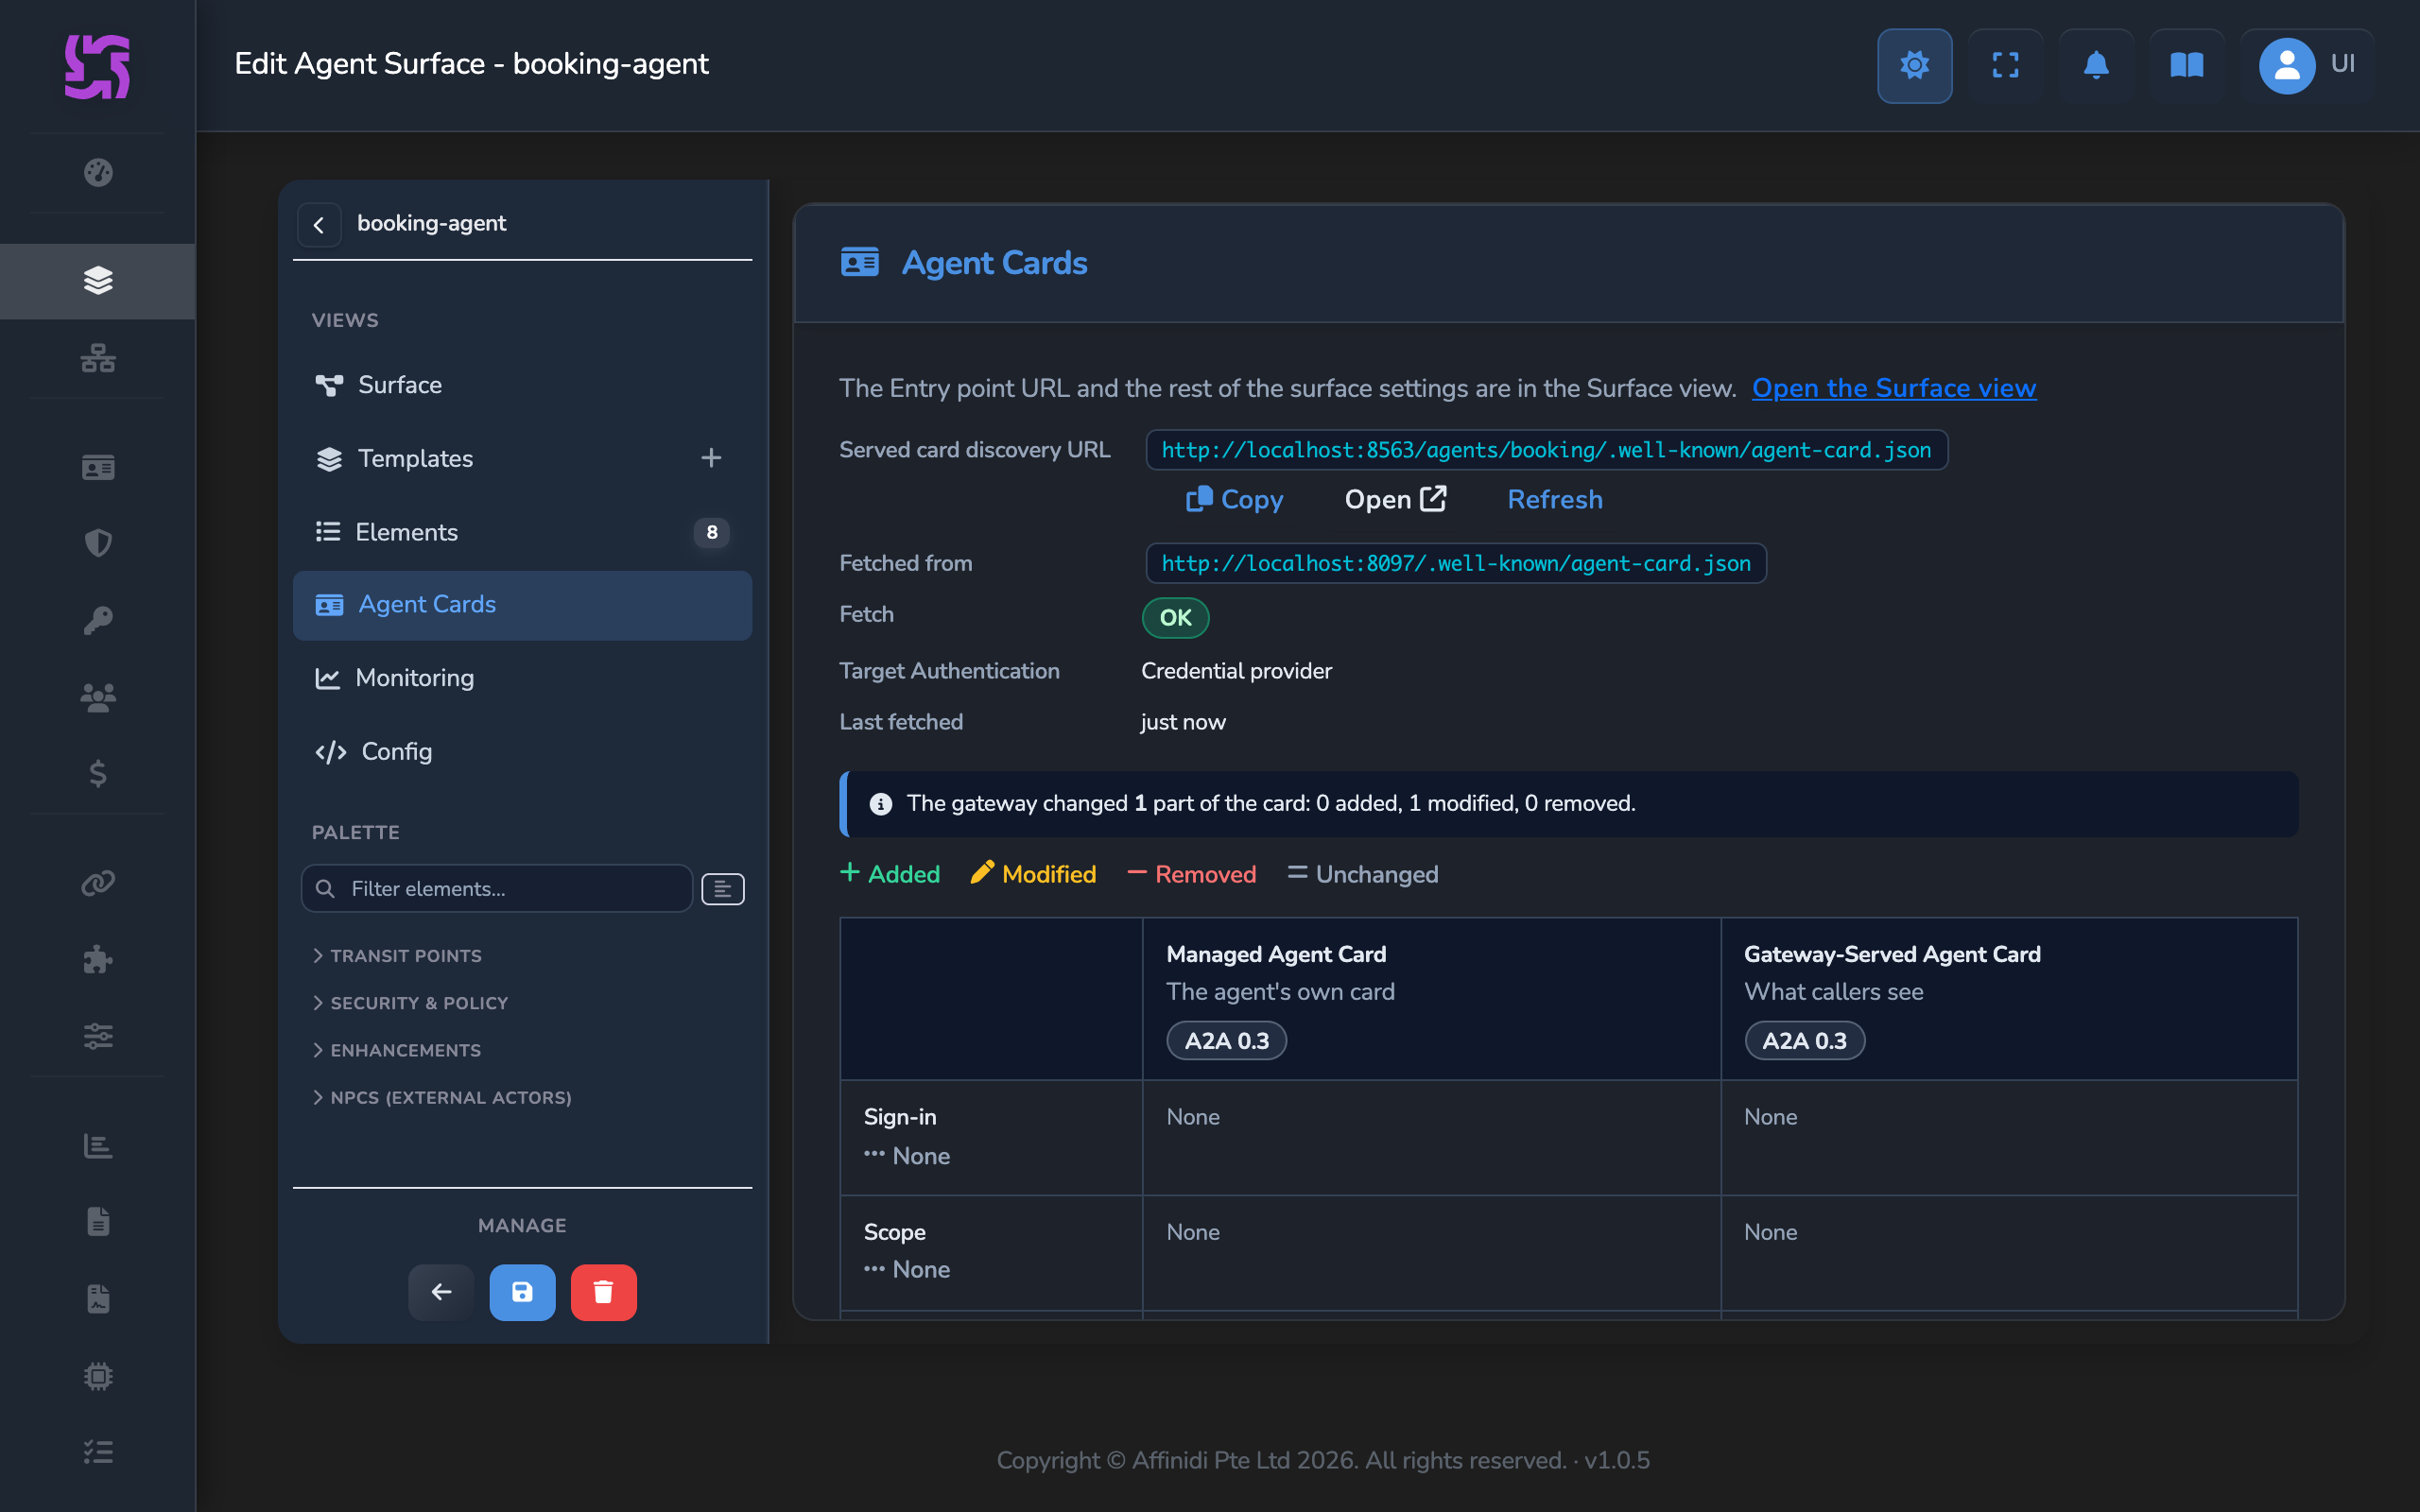
| Item | Description |
|---|---|
| Served card discovery URL | The URL where callers read the card the gateway serves, with Copy, Open, and Refresh. Refresh fetches the card again and needs permission to edit surfaces. |
| Fetched from | The agent card URL the gateway fetched. |
| Fetch | OK, Failing, or Not served, with the cause of a failure. |
| Target Authentication | What the gateway sent with the fetch, for example No Target Authentication, Static secret, or Credential provider. When the gateway couldn’t obtain the credential, it shows Credential not obtained. |
| Last fetched | When the gateway last fetched the card. |
| Managed Agent Card and Gateway-Served Agent Card | The card your agent publishes beside the card the gateway serves. Each difference is tagged Unchanged, Added, Modified, or Removed. |
When the fetch fails, the view explains the cause and what to check. For example, Needs a token means the agent asked for a token and the gateway sent none, so set Target Authentication on the Managed Agent. For a surface behind an A2A proxy, the gateway generates the card, so there is no agent card to compare.
Canvas elements on the Managed Agent
The following elements can be added to the surface from the element palette. Each appears as its own node on the canvas and attaches to the Managed Agent’s edges.
| Element | Description |
|---|---|
| Caller Context | Extracts caller authentication context from inbound callers (JWT, API key, DID Auth, mTLS). See Caller Context element reference. |
| Policy | OPA policy evaluation gate. Can be placed on the request or response edge. See Policy element reference. |
| Rate Limit | Per-route or per-caller request rate limiting. See Rate Limit element reference. |
| Payment | x402 or MPP paywall (MCP and A2A surfaces only). See Payment element reference. |
| Identity | Extracts agent DID from inbound or outbound traffic for VP stamping. See Identity element reference. |
| Trust Check | Runs a TRQP authorisation or recognition query against a trust registry. On the Managed Agent’s own target leg, available only when Endpoint Type is via A2A Proxy or via Gateway Connection. See Trust registry elements reference. |
| Trust Recorder | Writes agent-registration records into one or more trust registries. See Trust registry elements reference. |
| Extension Validation | Requires and validates protocol extensions on requests (A2A only). See Protocol extension elements reference. |
| Extension Rules | Allows, strips, or rejects protocol extensions per URI (A2A only). See Protocol extension elements reference. |
| Metadata Injection | Injects custom request or response headers, extensions, or body fields. See Metadata elements reference. |
| Metadata Extraction | Maps request headers into protocol metadata before downstream controls run. See Metadata elements reference. |
| Credential Delegation | Injects outbound credentials for upstream calls. See Outbound binding elements reference. |
| Workload Binding | Binds managed-agent identity and caller context into the outbound VP for a Transit Point. See Outbound binding elements reference. |
| Per-tool policy bindings | Per-tool OPA policy bindings configured on the node labelled MCP Proxy in the synthesised chain, not a draggable canvas element. See Per-tool policy bindings reference. |
| MCP Tool Gating | Regex-based allow/deny firewall over MCP tool names, applied to both tools/list and tools/call (MCP surfaces only). See MCP Tool Gating element reference. |
| Networking | Timeout, retry, circuit breaker, and traffic mirroring. See Networking element reference. |
Endpoint schemes
| Scheme | Format | Use case |
|---|---|---|
| HTTPS | https://<host>:<port>/<path> | Standard HTTP/S upstream target. |
| Fabric | fabric://{gateway_id}/{surface_id} | Gateway-to-gateway routing through the fabric. |
| Proxy | proxy://{mcp_proxy_id} | Routes through a configured MCP proxy backend. Requires mcp_proxy_id. |
| A2A Proxy | a2a-proxy://{a2a_proxy_id} | Routes through a configured A2A proxy backend. Available on A2A surfaces. |
Related
- Access Point reference: Inbound configuration and caller authentication.
- Transit Points reference: Agent-initiated outbound routes.
- Credentials: Credential provider types, including the ones Target Authentication can use.
- Trust registry elements reference: Full field reference for Trust Check and Trust Recorder elements.
- OPA policies concepts: How gateway and surface-level OPA policies are evaluated.
Glad to hear it. Thanks for letting us know.
Sorry to hear that. Thanks for letting us know.
Still stuck? Ask the community on Discord or contact us.